password-authentication
 Sue mackin
Input Target you control Test username(s) A locally generated test password list Optional concurrency settings Candidate generator Generates or reads candidate passwords. Common approaches are dictionary, rule-based, and exhaustive combinations. Attempt engine Sends each candidate to a deliberately vulnerable local test authentication service. Records whether the laboratory service accepts or rejects it. Response analyzer Determines success/failure from the controlled test application's response. Real-world tools can use HTTP status codes and response contents, although relying on only status codes can produce false positives. Concurrency/queue A worker pool processes candidates. A central queue tracks pending, successful, and failed attempts. Results Attempts/second Number tested Successful laboratory credential Error counts Runtime/logs

Comments (0)
Sign in to leave a comment
Project Tasks
27 planning tasksGenerate system requirement document
Generate personas & user flows
Create flow for Laboratory Operator
Landing
Fix Landing review findings: Q1 as reviewed now: Mobile page still overflows… (+1 more)
Fix Landing review finding: Measured horizontal overflow at mobile: the page is 535px…
Fix Landing review findings: The second hero line wraps into an unintended third line… (+1 more)
Landing / Top Bar
Landing / Hero Headline
Landing / Instrument Panel
Landing / Constraint Statement
Landing / Footer
Footer
Run Configuration
Run Configuration / Top Bar
Run Configuration / Form
Run Configuration / Footer
Candidates
Candidates / Top Bar
Candidates / Generator Panel
Candidates / Footer
Queue
Run
Analysis
Results
Architecture
Workspace task plan
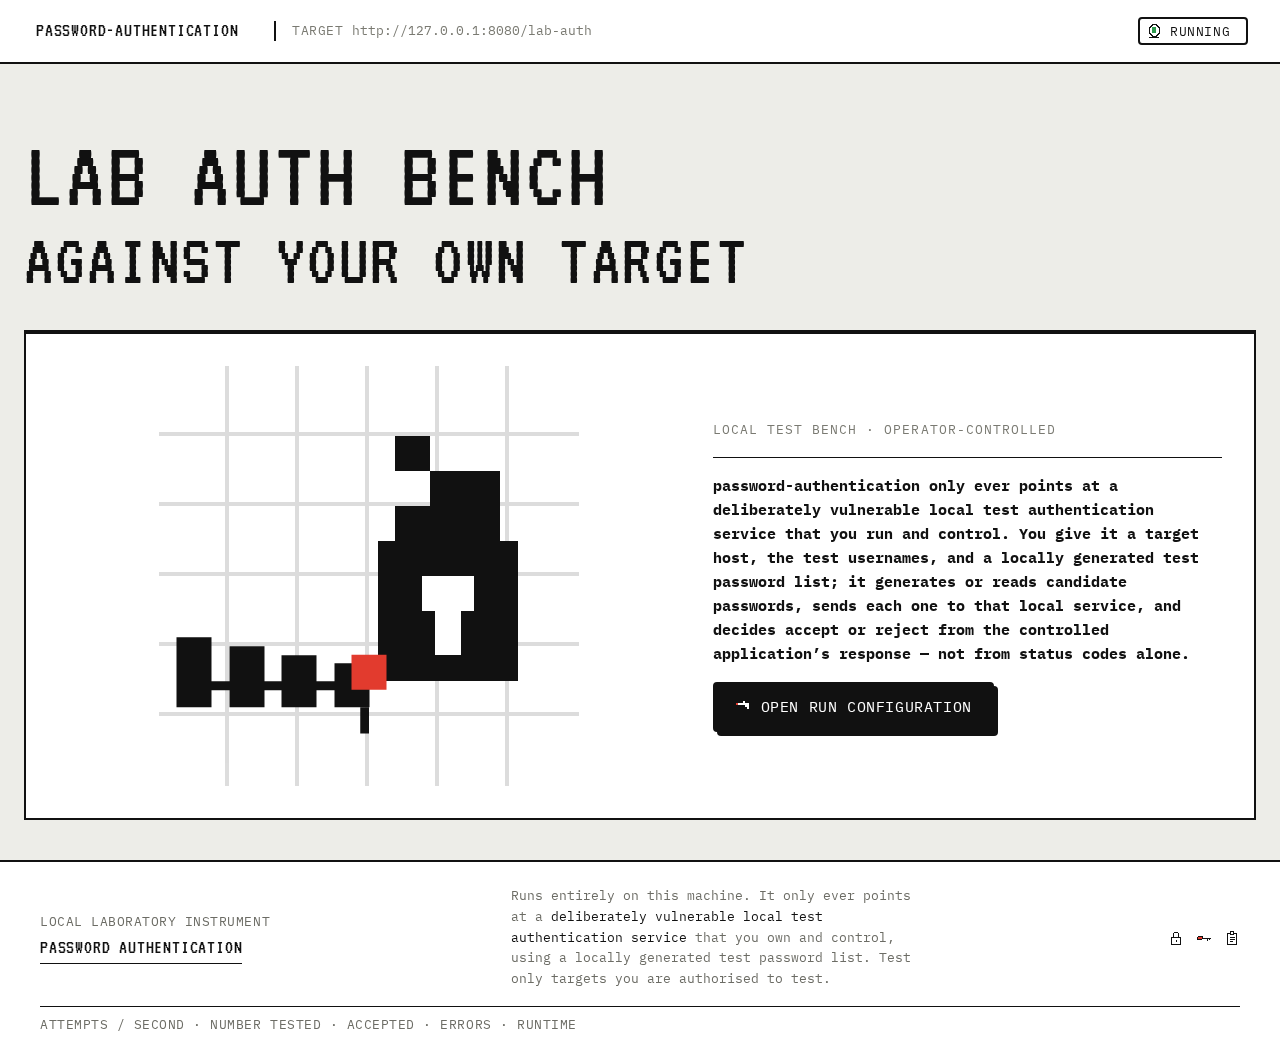
LAB AUTH BENCH
AGAINST YOUR OWN TARGET
Local test bench · operator-controlled
password-authentication only ever points at a deliberately vulnerable local test authentication service that you run and control. You give it a target host, the test usernames, and a locally generated test password list; it generates or reads candidate passwords, sends each one to that local service, and decides accept or reject from the controlled application’s response — not from status codes alone.
Open Run ConfigurationLAB AUTH BENCH
AGAINST YOUR OWN TARGET
Local test bench · operator-controlled
No comments yet. Be the first!