local-test
 Hello Mcdonald
┌──────────────────┐ │ Local Test Target│ └────────┬─────────┘ │ HTTP/API request │ ┌─────────────┐ ┌───▼────────┐ │ Test Inputs │──►│ Attempt │ └─────────────┘ │ Controller │ └─────┬───────┘ │ ┌──────▼──────┐ │ Candidate │ │ Generator │ └──────┬──────┘ │ ┌──────▼──────┐ │ Worker Pool │ └──────┬──────┘ │ ┌──────▼──────┐ │ Local Test │ │ Auth Server │ └──────┬──────┘ │ ┌──────▼──────┐ │ Result/Log │ └─────────────┘


Comments (0)
Sign in to leave a comment
local-test
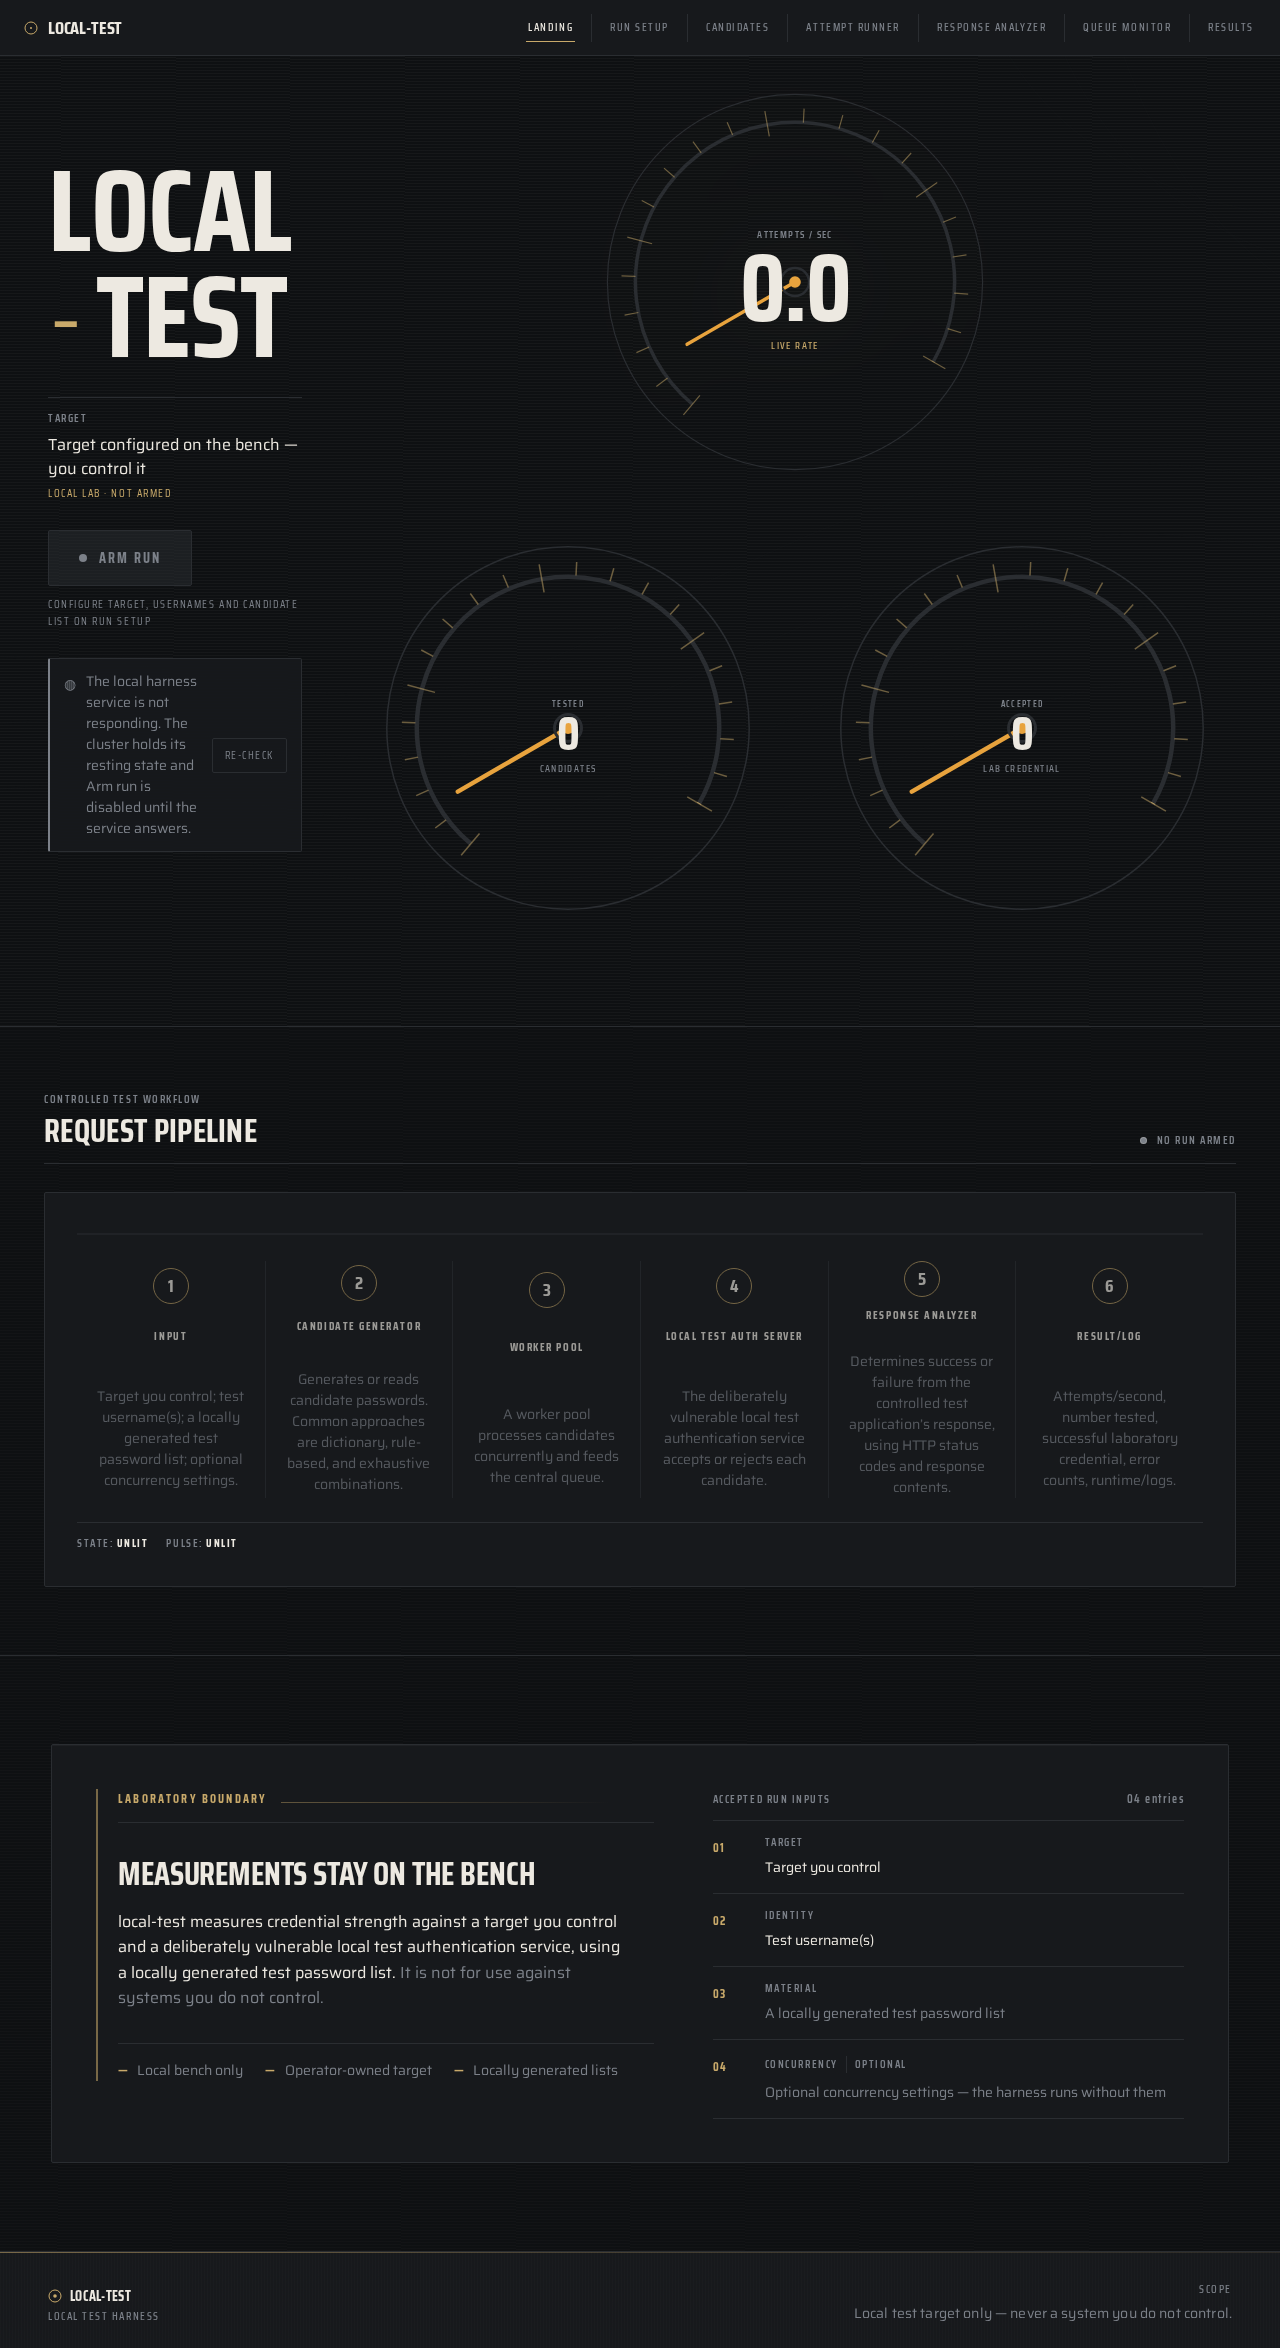
Configure target, usernames and candidate list on Run Setup
Request pipeline
- 1Input
Target you control; test username(s); a locally generated test password list; optional concurrency settings.
- 2Candidate Generator
Generates or reads candidate passwords. Common approaches are dictionary, rule-based, and exhaustive combinations.
- 3Worker Pool
A worker pool processes candidates concurrently and feeds the central queue.
- 4Local Test Auth Server
The deliberately vulnerable local test authentication service accepts or rejects each candidate.
- 5Response Analyzer
Determines success or failure from the controlled test application’s response, using HTTP status codes and response contents.
- 6Result/Log
Attempts/second, number tested, successful laboratory credential, error counts, runtime/logs.
Measurements stay on the bench
local-test measures credential strength against a target you control and a deliberately vulnerable local test authentication service, using a locally generated test password list. It is not for use against systems you do not control.
No comments yet. Be the first!