APKSIELD
 Shaguftha Kulsum
Based on the attached APKSHIELD synopsis for CIDECODE Hackathon 2026, build a COMPLETE FULL-STACK WEB APPLICATION called APKSHIELD — an India-specific APK Threat Analysis Platform with C2 Detection for cybercrime investigators. Build an actual working application, not a UI mockup or demo. Use: Frontend: - React.js - Tailwind CSS - D3.js - WebSockets Backend: - Python 3.11 - FastAPI - Celery - Redis Database & Storage: - PostgreSQL - SQLAlchemy - MinIO APK Analysis: - androguard - apktool - JADX - Frida - Android Emulator/AVD - mitmproxy - tshark - scapy - YARA - scikit-learn Threat Intelligence: - VirusTotal API - AbuseIPDB - Shodan - MISP Implement: - JWT authentication - APK upload system - Static APK analysis - Dynamic sandbox analysis - Permission extraction - URL/IP extraction - Firebase-as-C2 detection - Telegram bot token extraction - Runtime API hooking - PCAP generation - DNS logging - Beaconing detection - IOC extraction - MITRE ATT&CK mapping - Threat scoring engine - Malware classification - D3.js infrastructure graph - Real-time WebSocket logs - FIR-ready PDF forensic reports - Evidence chain logging - Investigator dashboard - Role-based access control Make the platform India-specific by including: - fake Indian banking app detection - SBI/HDFC/ICICI/Paytm/PhonePe spoof detection - Aadhaar/IRCTC phishing APK detection - Indian cybercrime investigation workflows - FIR-ready reporting format Generate: - full frontend - full backend - API routes - database schema - Docker setup - Docker Compose - Celery workers - WebSocket implementation - reusable architecture - setup instructions - README.md The final output should resemble a real SOC-grade malware investigation platform used by Indian cybercrime investigators and must be fully runnable locally using Docker.


Comments (0)
Sign in to leave a comment
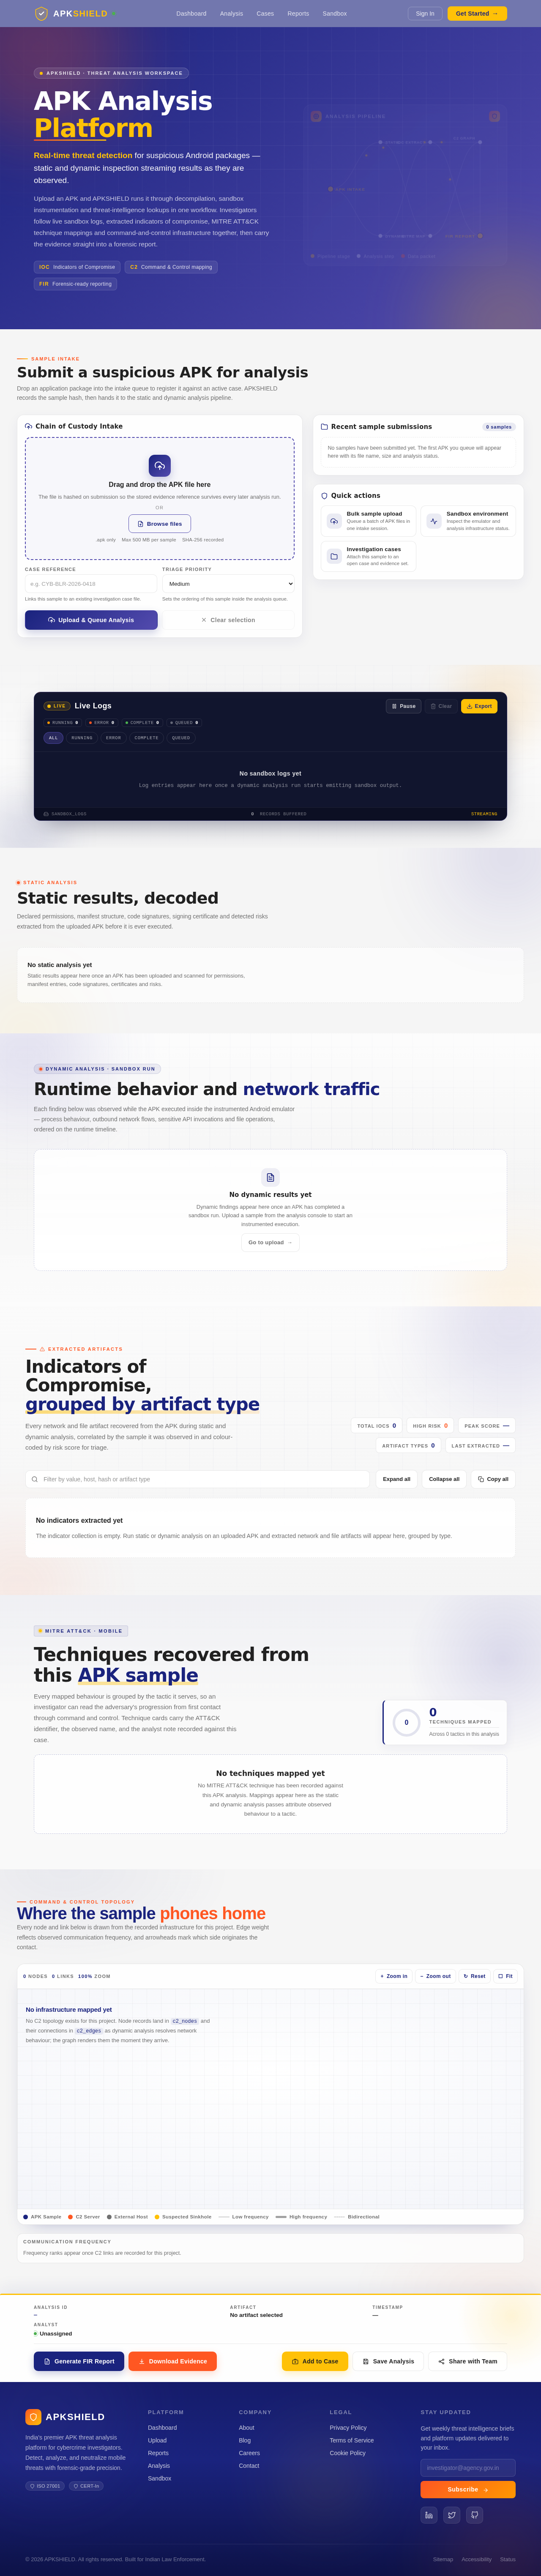
APK Analysis Platform
Real-time threat detection for suspicious Android packages — static and dynamic inspection streaming results as they are observed.
Upload an APK and APKSHIELD runs it through decompilation, sandbox instrumentation and threat-intelligence lookups in one workflow. Investigators follow live sandbox logs, extracted indicators of compromise, MITRE ATT&CK technique mappings and command-and-control infrastructure together, then carry the evidence straight into a forensic report.
- IOCIndicators of Compromise
- C2Command & Control mapping
- FIRForensic-ready reporting
Submit a suspicious APK for analysis
Drop an application package into the intake queue to register it against an active case. APKSHIELD records the sample hash, then hands it to the static and dynamic analysis pipeline.
Chain of Custody Intake
Drag and drop the APK file here
The file is hashed on submission so the stored evidence reference survives every later analysis run.
orRecent sample submissions
0 samplesNo samples have been submitted yet. The first APK you queue will appear here with its file name, size and analysis status.
Live Logs
Static results, decoded
Declared permissions, manifest structure, code signatures, signing certificate and detected risks extracted from the uploaded APK before it is ever executed.
Runtime behavior and network traffic
Each finding below was observed while the APK executed inside the instrumented Android emulator — process behaviour, outbound network flows, sensitive API invocations and file operations, ordered on the runtime timeline.
No dynamic results yet
Dynamic findings appear here once an APK has completed a sandbox run. Upload a sample from the analysis console to start an instrumented execution.
Go to uploadIndicators of Compromise, grouped by artifact type
Every network and file artifact recovered from the APK during static and dynamic analysis, correlated by the sample it was observed in and colour-coded by risk score for triage.
No indicators extracted yet
The indicator collection is empty. Run static or dynamic analysis on an uploaded APK and extracted network and file artifacts will appear here, grouped by type.
Techniques recovered from this APK sample
Every mapped behaviour is grouped by the tactic it serves, so an investigator can read the adversary's progression from first contact through command and control. Technique cards carry the ATT&CK identifier, the observed name, and the analyst note recorded against this case.
No techniques mapped yet
No MITRE ATT&CK technique has been recorded against this APK analysis. Mappings appear here as the static and dynamic analysis passes attribute observed behaviour to a tactic.
Where the sample phones home
Every node and link below is drawn from the recorded infrastructure for this project. Edge weight reflects observed communication frequency, and arrowheads mark which side originates the contact.
No infrastructure mapped yet
No C2 topology exists for this project. Node records land in c2_nodes and their connections in c2_edges as dynamic analysis resolves network behaviour; the graph renders them the moment they arrive.
- APK Sample
- C2 Server
- External Host
- Suspected Sinkhole
- Low frequency
- High frequency
- Bidirectional
Communication frequency
Frequency ranks appear once C2 links are recorded for this project.
India's#1APKThreatAnalysisPlatform
Empowering Indian cybercrime investigators with forensic-grade APK analysis. Detect malware, extract IOCs, map C2 infrastructure, and generate FIR-ready reports — all from a single platform.
India Threat Map
Real-time APK threat levels across Indian states. Hover over regions to see active threats, or click to zoom into regional analysis.
Click on any region to zoom into regional analysis
Key Features
Comprehensive investigative tools purpose-built for Indian cybercrime units. From decompilation to court-ready reports — everything in one platform.
Static Analysis
Decompile and inspect APK manifests, permissions, embedded URLs, hardcoded credentials, and suspicious code patterns without executing the application.
Learn more→Dynamic Analysis
Execute APKs in isolated sandbox environments to monitor runtime behavior, network calls, file system changes, and privilege escalation attempts.
Learn more→IOC Extraction
Automatically extract Indicators of Compromise including domains, IPs, hashes, and registry keys mapped to known threat intelligence feeds.
Learn more→MITRE ATT&CK Mappings
Map discovered techniques to the MITRE ATT&CK Mobile framework for standardized threat classification and cross-case correlation.
Learn more→C2 Detection
Identify Command & Control infrastructure through traffic analysis, DGA detection, and encrypted channel fingerprinting linked to active threat actors.
Learn more→FIR Report Generation
Generate court-admissible First Information Reports with forensic evidence chains, MITRE references, and compliance-ready documentation for Indian law enforcement.
Learn more→Forensic-Grade Analysis Capabilities
APKSHIELD integrates industry-leading reverse engineering tools into a unified pipeline — from static decompilation to live runtime instrumentation.
- Androguard IntegrationDeep APK manifest parsing, permission analysis, and component enumeration for static threat assessment.
- JADX DecompilationFull Java/Kotlin source recovery from DEX bytecode with obfuscation-aware class resolution.
- Frida Dynamic InstrumentationRuntime hooking of crypto APIs, network calls, and native functions inside sandboxed emulators.
- YARA Rule MatchingPattern-based detection against 12,000+ signatures including India-specific banking trojan rules.
- Network Traffic AnalysisCapture and decode TLS-intercepted traffic to identify C2 servers, data exfiltration, and SMS gateways.
- MITRE ATT&CK MappingAutomated technique classification mapped to mobile ATT&CK framework with confidence scoring.
See Real-Time Analytics in Action
Monitor threat intelligence, APK analyses, and live investigation logs as they happen across India's cybercrime landscape.
What Cyber Crime Units Say
Law enforcement teams across India rely on APKSHIELD to accelerate investigations, strengthen evidence, and protect citizens from mobile threats.
Plans Built for Investigation Teams
Choose the right level of threat analysis power for your unit. All plans include core APK scanning and reporting capabilities.
Investigator
For individual cyber-crime officers running solo APK investigations.
Billed monthly, cancel anytime
What's included- Up to 50 APK scans per month
- Static analysis & threat scoring
- IOC extraction & YARA rules
- Basic forensic report generation
- MITRE ATT&CK mapping
- Email support (48hr SLA)
- Dynamic sandbox analysis
- Team case management
- Custom threat intelligence feeds
Team
For cyber-crime cells and investigation units needing collaborative tools.
Billed monthly, cancel anytime
What's included- Unlimited APK scans
- Static + dynamic analysis
- Advanced IOC & C2 infrastructure graphs
- FIR-ready forensic reports
- MITRE ATT&CK + CERT-In mapping
- Team case management (up to 15 users)
- Priority support (4hr SLA)
- Regional threat intelligence feeds
- Custom YARA rule builder
Enterprise
For state-level agencies and large organizations with dedicated infrastructure.
Tailored to your organization
What's included- Everything in Team, plus:
- Unlimited users & departments
- On-premise deployment option
- Dedicated sandbox cluster
- Custom API integrations
- White-label reporting
- Dedicated account manager
- 24/7 phone & on-site support
- SLA-backed uptime guarantee (99.9%)
All plans include SSL encryption, CERT-In compliant data handling, and 99.5% uptime. Need a custom plan? Talk to our team.
Enterprise Security & Compliance
APKSHIELD meets the highest security and regulatory standards required by Indian law enforcement agencies, ensuring your forensic data remains protected and legally admissible.
APKSHIELD maintains ISO 27001 certification, ensuring systematic management of sensitive data with rigorous access controls and audit trails.
End-to-End Encryption
AES-256 encryption for data at rest and TLS 1.3 for data in transit. Zero-knowledge architecture ensures only authorized investigators access case files.
SOC 2 Type II Audit
Annual third-party audits verify our security controls, availability, and confidentiality meet enterprise-grade standards for government agencies.
GDPR & DPDP Ready
Built-in compliance with India's Digital Personal Data Protection Act and international privacy frameworks for cross-border investigations.
Chain of Custody
Tamper-proof evidence logging with SHA-256 hashing, timestamped audit trails, and FIR-ready forensic reports accepted by Indian courts.
Ready to Analyze Threats?
Join hundreds of Indian law enforcement agencies using APKSHIELD to detect, analyze, and neutralize mobile threats with forensic-grade precision. Start your investigation in minutes.
No comments yet. Be the first!